


This tutorial shows you how to install an SSL certificate on Windows Server with IIS using AutoInstall SSL, the agent included with SSL Dragon’s RapidSSL and GeoTrust automation plans. You run one command to install the agent and one to request, validate and bind the certificate in IIS. From then on, the agent renews the certificate and updates the binding on its own.
Setup usually takes under 15 minutes, most of it waiting for the Certificate Authority to validate your domain.
Before you start
- An active AutoInstall plan. Any of the four AutoInstall SSL plans works: RapidSSL Standard, RapidSSL Wildcard, GeoTrust QuickSSL Premium or GeoTrust QuickSSL Premium Wildcard.
- Windows Server 2016, 2019, 2022 or 2025 running IIS, on a dedicated server, VPS or cloud VM.
- Administrator access to the server, usually over Remote Desktop. The agent installs into C:\Program Files, changes the system PATH and creates scheduled tasks, so every command below needs an elevated window.
- An IIS site with a host name binding for your domain. The agent finds the site by its binding. In IIS Manager, open the site, click Bindings and make sure there is an http binding on port 80 whose Host name is your domain. If you want the certificate to cover www as well, add a second binding for www.example.com.
- DNS pointing at this server and port 80 reachable. The default file validation places a file under http://example.com/.well-known/pki-validation/ and the Certificate Authority fetches it from the internet. Allow inbound TCP 80 and 443 in Windows Defender Firewall and in any cloud firewall or security group in front of the server.
Wildcard plans cannot use file validation. They need DNS validation through your DNS provider’s API, covered in Wildcard certificates and DNS validation below.
Install an SSL certificate on IIS with AutoInstall SSL
Step 1: Create the AutoInstall subscription in your account
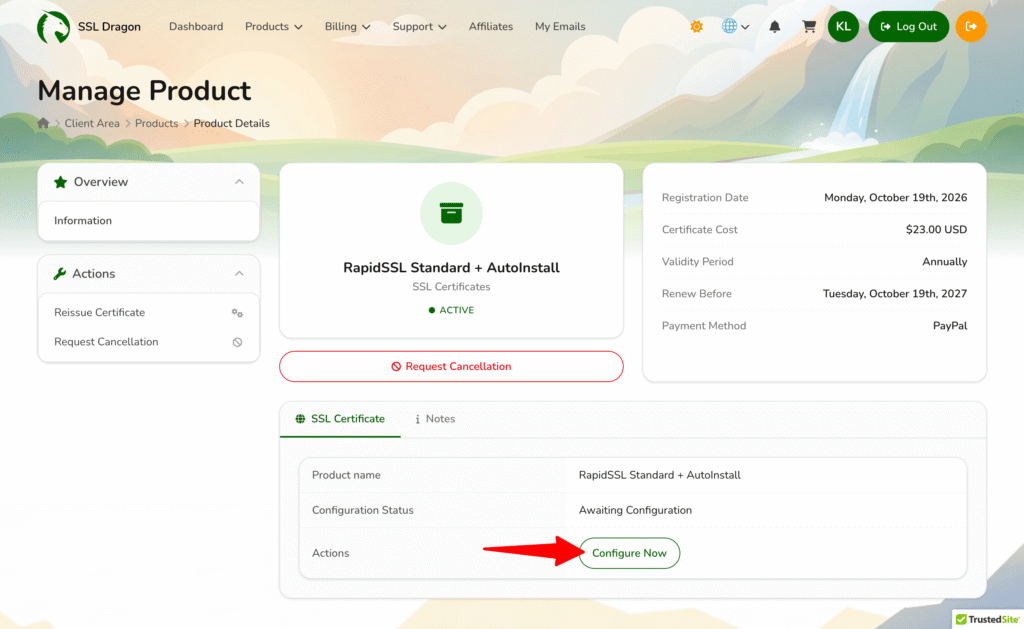
- Log in to your SSL Dragon account and open the AutoInstall product from Services.
- On the SSL Certificate tab, Configuration Status reads Awaiting Configuration. Click Configure Now to open the AutoInstall SSL Configuration form.

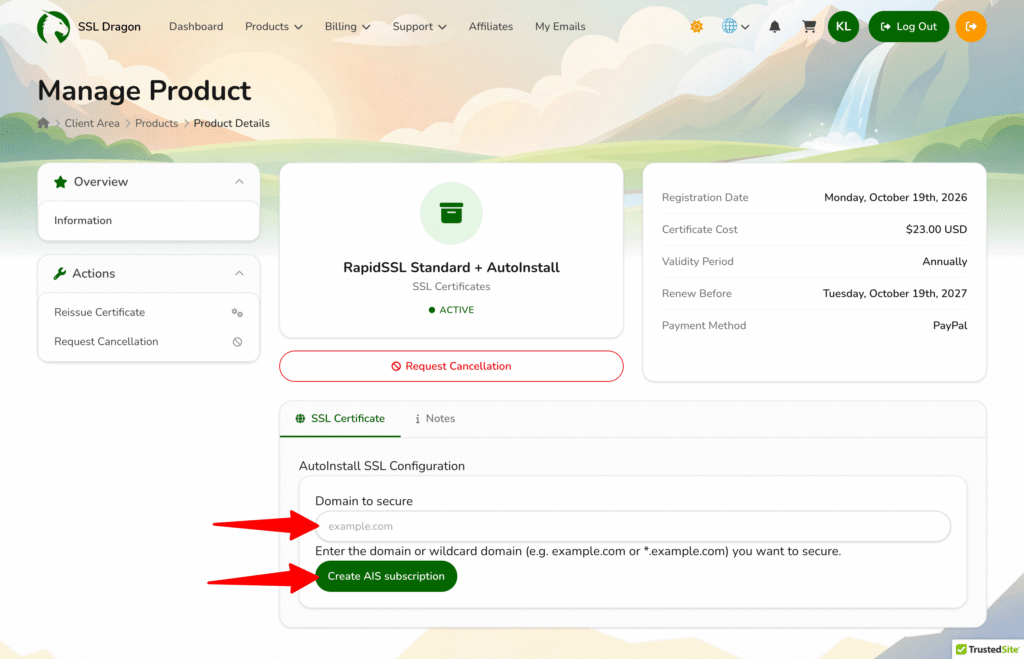
- In Domain to secure, enter your domain without www (for example, example.com). For a wildcard plan, enter *.example.com.
- Click Create AIS subscription.

The SSL Certificate tab now shows the order details, with AutoInstall status showing Incomplete until the certificate is installed (it changes to Issued afterwards), and two buttons:
- Get started / Login opens the installation instructions on autoinstallssl.app, with your personal commands.
- Manage AutoInstall SSL opens the management page, where you track the certificate afterwards.
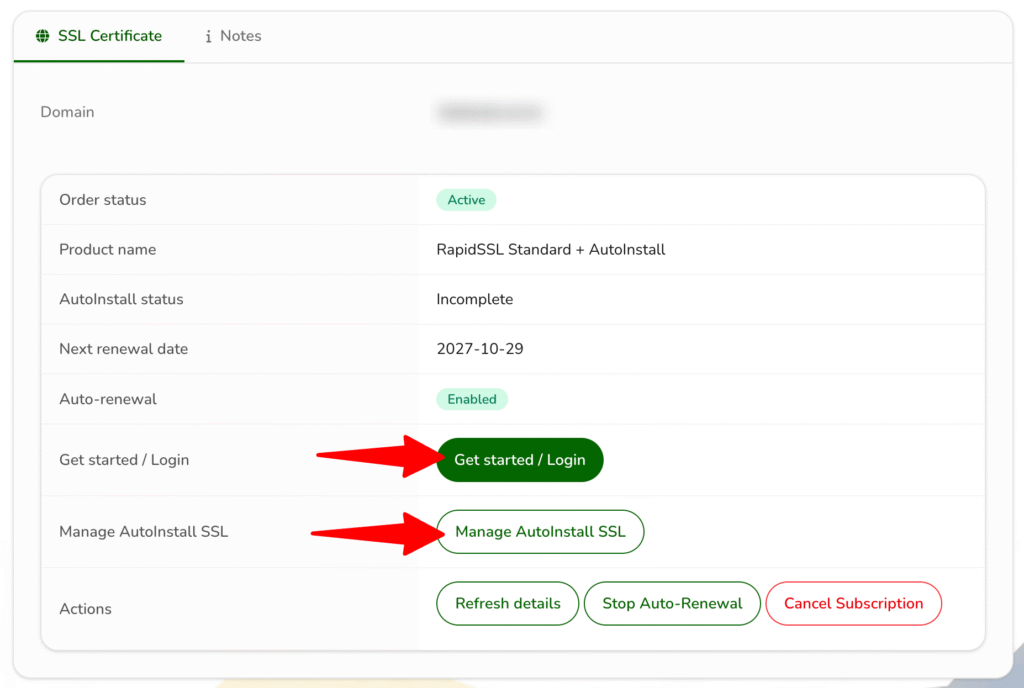
Keep your token private. The install command contains a token tied to your order. Anyone who has it can install your certificate on their own server.
Step 2: Choose IIS and your validation options
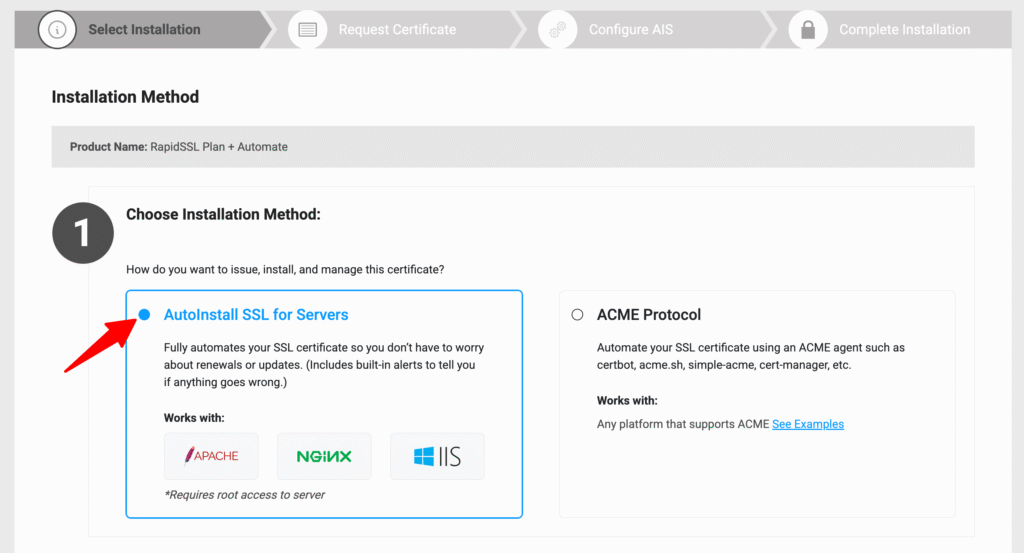
Click Get started / Login. If the page first asks you to Choose Installation Method, select AutoInstall SSL for Servers and click Continue. (The other option, ACME Protocol, is for ACME clients such as Certbot and is not covered here.)
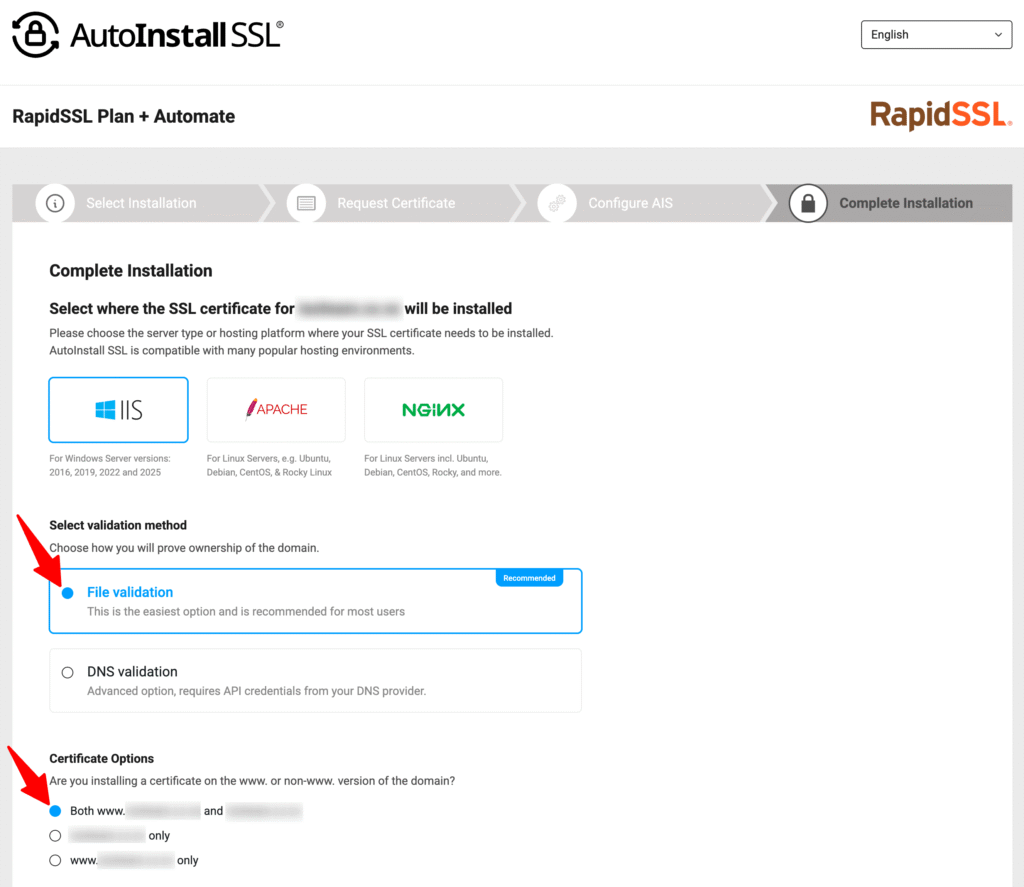
Under Complete Installation, make three choices. The page saves them with your order:
- Server type: select IIS.
- Validation method: keep File validation (recommended) unless you have a wildcard plan or the server is not reachable from the internet on port 80.
- Certificate options: choose whether to cover both www.example.com and example.com, only the bare domain, or only the www version.
The page updates both commands to match your choices. The www option becomes a flag in the install command: --includewww for both names, --onlywww for the www version only, and no flag for the bare domain.
Step 3: Install the agent
Connect to the web server over Remote Desktop. Right-click the Start button, choose Terminal (Admin) or Windows PowerShell (Admin), and accept the User Account Control prompt if one appears. Then paste the agent command from the instructions page. It is the same for every Windows order:
powershell -Command "& { [Net.ServicePointManager]::SecurityProtocol = [Net.SecurityProtocolType]::Tls13 -bor [Net.SecurityProtocolType]::Tls12; iwr -useb https://files.autoinstallssl.com/packages/windows/version/latest/Win-AutoInstallSSL.ps1 | iex; }"The first part switches PowerShell to TLS 1.2 or 1.3 so the download also works on older Windows Server builds. The installer then:
- Downloads the agent and extracts it to C:\Program Files\AutoInstallSSL\aisagent.
- Adds that folder to the system PATH, so AutoInstallSSL.exe runs from any directory in new windows.
- Writes its own log to C:\Program Files\AutoInstallSSL\Log.
- Opens a new Command Prompt as administrator, already inside the agent folder. If Windows asks for permission again, click Yes.
If the window you used was not elevated, the installer stops with an Administrator Privileges Required message box. Close it, open an elevated window and run the command again.
Step 4: Run the certificate install command
Switch to the new Command Prompt window the installer opened. Your original window started before the PATH changed, so it may not find AutoInstallSSL.exe. Paste the second command from the instructions page. It already contains your token. For file validation covering both www and the bare domain, it looks like this:
AutoInstallSSL.exe installcertificate --token YOUR_TOKEN --includewww --validationtype file --validationprovider filesystem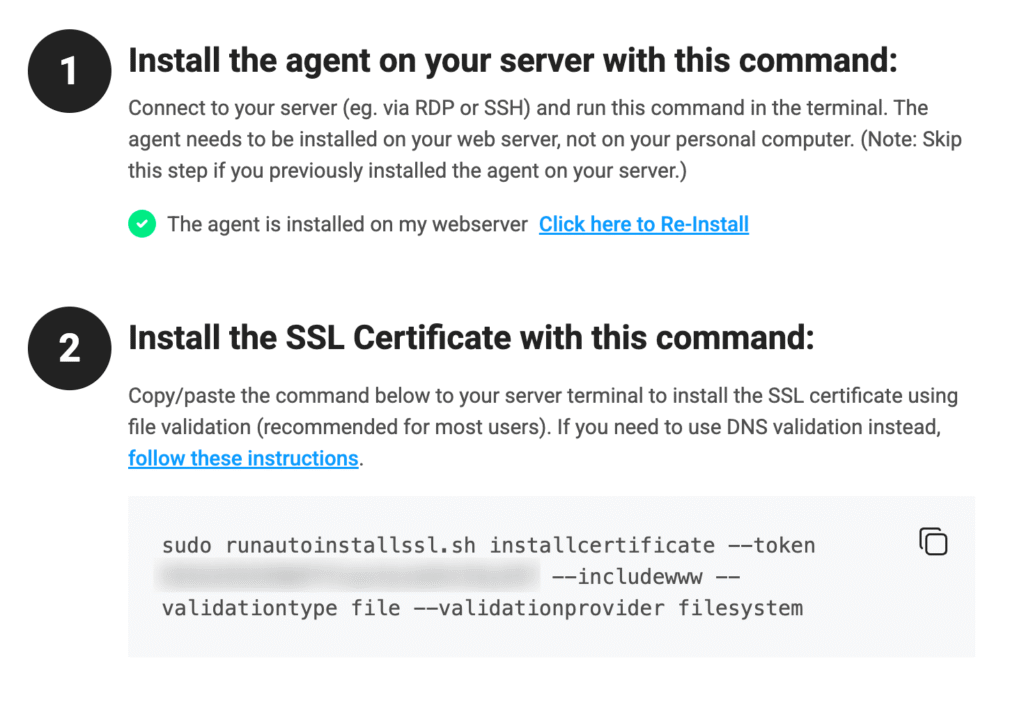
The agent then works through these stages:
- Scans the server. It checks for administrator rights and detects IIS, then finds the IIS site whose binding matches your domain.
- Asks you to confirm. It prints the site, bindings and validation settings it will use and asks Do you want to continue with the installation process? Check the details and type y.
- Validates the domain. It creates the private key and CSR on the server, places the validation file in the site’s folder and runs its own pre-check. You should see Passed preliminary validation check, waiting for the certificate authority to complete comprehensive validation checks (typically takes 1-10 minutes).
- Installs the certificate. It imports the issued certificate into the Web Hosting certificate store of the local computer, then adds an https binding on port 443 based on your existing http binding. If the site already has an https binding, the agent updates it to the new certificate instead.
- Schedules renewals. It registers a scheduled task named AutoInstallSSL reissue.
The run ends with a line that starts Success! Certificate and ends has been successfully installed. The private key stays on the server and is marked as non-exportable by default.
Step 5: Check the installation
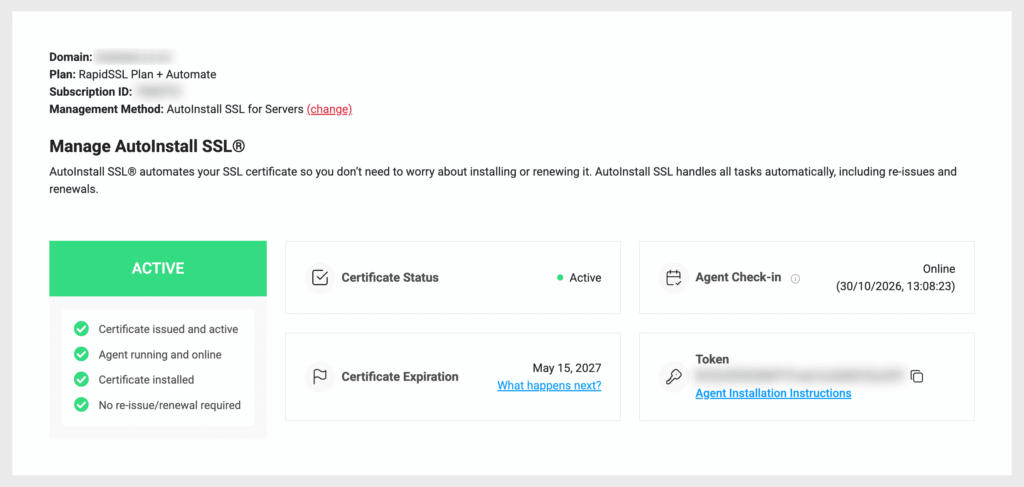
The management page. Status should read ACTIVE, with Certificate issued and active, Agent running and online, Certificate installed and No re-issue/renewal required. Agent Check-in shows Online with the time of the last contact.
IIS Manager. Open the site, click Bindings, select the https binding and click Edit. The SSL certificate drop-down should show the new certificate.
The agent. In an elevated window, list the certificates it manages:
AutoInstallSSL.exe viewcertificatesFrom outside. Run your domain through our SSL Checker to confirm the certificate, the chain and the expiry date that visitors see.
Looking for the certificate in certlm.msc? It is under Web Hosting, not Personal, which is where most people look first.
The agent adds HTTPS but does not remove plain HTTP. To send every visitor to HTTPS, add a redirect rule in IIS. See how to redirect HTTP to HTTPS.
For every command the agent accepts, see AutoInstall SSL agent commands.
How automatic renewal works
The agent creates two scheduled tasks. AutoInstallSSL reissue checks the certificate twice a day, starting in the early morning with a random delay so not every server calls in at once. AutoInstallSSL autoupdate keeps the agent itself up to date once a day. Check that both exist with:
Get-ScheduledTask -TaskName "AutoInstallSSL*"When the certificate is 28 days from expiry, the agent requests a new one, validates the domain again, imports it and switches the https binding over to the new certificate.
This matters more each year. Public SSL certificates are limited to 200 days since March 2026, 100 days from March 2027 and 47 days from March 2029. AutoInstall SSL handles every replacement within your subscription, so the shorter lifetimes add no work.
Two things stop renewals: an expired or cancelled subscription, and a disabled or deleted scheduled task. Keep Auto-renewal showing Enabled on the product’s SSL Certificate tab in your SSL Dragon account, and leave both tasks enabled.
To change the renewal window, run AutoInstallSSL.exe without arguments to open its menu, pick Settings & Credentials (option 4), then Manage configuration. Renewal Days accepts 1 to 28. Keep it at 28, the recommended value, which suits almost everyone because it leaves the most time to fix a problem before the certificate expires.
Wildcard certificates and DNS validation
Wildcard plans require DNS validation. If you try file validation, the agent stops with File validation will not work for wildcard order. Please select dns for it. The www options do not apply either, since *.example.com already covers www.
With DNS validation, the agent creates the validation record through your DNS provider’s API, so it needs API credentials. Supported providers include Cloudflare, GoDaddy, AWS Route 53, Azure DNS, Google Cloud DNS, DigitalOcean, DNS Made Easy, Name.com, Namecheap, OVH and any DNS server that accepts RFC 2136 updates.
Select DNS validation on the instructions page and copy the command it generates. For Cloudflare, it follows this pattern:
AutoInstallSSL.exe installcertificate --token YOUR_TOKEN --validationtype dns --validationprovider cloudflare --cloudflareapitoken YOUR_CLOUDFLARE_API_TOKENFor Cloudflare, create an API Token, not the Global API Key. Start from the Edit zone DNS template, set Zone Resources to All zones, and under Permissions add User > User Details > Read. The agent checks the token against your Cloudflare user and lists your zones to find the right one, so a token scoped to a single zone or missing a permission fails with an error such as No zones could be found using the Cloudflare API.
The agent stores the secret values encrypted on the server and reuses them at every renewal. If you rotate the key at your DNS provider, update it on the server too: run AutoInstallSSL.exe, choose Settings & Credentials, then Manage DNS provider credentials.
Troubleshooting
‚AutoInstallSSL.exe‘ is not recognized
The window was opened before the installer added the agent to the PATH. Use the Command Prompt the installer opened, open a new elevated window, or run the agent from its folder. The .\ prefix is required in PowerShell and also works in Command Prompt:
cd "C:\Program Files\AutoInstallSSL\aisagent"
.\AutoInstallSSL.exe viewcertificates
User does not have admin rights, or Unable to register scheduled task
Both messages mean the agent ran in a window without elevation. User does not have admin rights. Please log in with user having admin rights. stops the run before anything changes. Unable to register scheduled task, please run as administrator or equivalent is worse: the certificate may be installed but will not renew. In either case, run the install command again from an elevated window.
No site found, or Main domain binding not found
The agent could not match your domain to an IIS site. Add an http binding on port 80 with your domain as Host name to the right site, then run the install command again. WWW binding not found means you asked for www coverage but the site has no binding for www.example.com: add one, or drop --includewww. A message saying the site is bound to a non-supported port means the binding uses a port other than 80 or 443, which the agent does not support. Add a binding on port 80 or 443 for the domain.
Preliminary validation failed
The agent placed the validation file but could not read it back over the internet. Typical causes: the domain’s DNS points to another server, a firewall or cloud security group blocks port 80, or a proxy or CDN in front of the server answers instead. While the install command is waiting, it prints the exact URL after Validation value should now be browsable at. Open that URL from another machine. If it does not show the value the agent printed, fix the path between the internet and IIS, or switch to DNS validation.
Inactive agent or Agent Check-in shows offline
The agent has stopped reporting in, so renewals are not running. Check that the server is up and that the AutoInstallSSL reissue task exists and is enabled in Task Scheduler. If the site moved to a new server, install the agent there and run the install command again.
Collect logs for support
The diagnostic subcommand asks which dates you need and packs the agent’s event and error logs into a zip file, then prints where it saved it. Send that file to our support team with your order number. Installer and update logs are in C:\Program Files\AutoInstallSSL\Log.
AutoInstallSSL.exe diagnosticFrequently Asked Questions
No. The agent generates the private key and the CSR on the server during installation and at every renewal. You never use the Create Certificate Request wizard in IIS Manager.
The Web Hosting store of the local computer. Open certlm.msc and expand Web Hosting > Certificates to see it. IIS reads certificates from this store the same way it reads them from Personal.
Yes, through the agent rather than IIS. The certificate in the Web Hosting store has a non-exportable private key, but the agent keeps a password-protected PFX copy. Run AutoInstallSSL.exe without arguments, choose Get Help (option 3), then Get pfx password, and select your domain. The agent shows the PFX file path and its password.
Store the file as carefully as the private key it contains. Every renewal produces a new certificate, so a PFX copied to another system goes stale at the next renewal. Where possible, install the agent on the other server instead.
Yes. Install the agent once, then run the install command from each order’s instructions page. Each command carries that order’s token. Skip Step 3 for the second and later certificates.
The agent is built for IIS sites, and other Windows services are not among its supported environments. For those, every AutoInstall plan also supports ACME: on the management page, click (change) next to Management Method, choose ACME Protocol and use an ACME client such as simple-acme (the successor to win-acme). See also our ACME tutorials.
Run the official uninstall script from an elevated PowerShell window and click Yes when it asks you to confirm. It removes both scheduled tasks and the C:\Program Files\AutoInstallSSL folder.[Net.ServicePointManager]::SecurityProtocol = [Net.SecurityProtocolType]::Tls12; iwr -useb https://files.autoinstallssl.com/packages/windows/version/latest/Uninstall-AutoInstallSSL.ps1 | iex
Two harmless leftovers remain: the agent’s settings folder C:\ProgramData\AutoInstallSSL, and the C:\Program Files\AutoInstallSSL\aisagent entry in the system PATH, which the script does not remove. Delete them by hand if you want a clean server.
The certificate stays in the Web Hosting store and the https binding stays in IIS, so the site keeps working until the certificate expires. Nothing renews it after that.
Running Apache or NGINX on Linux instead? Follow our guide on installing an SSL certificate on Linux with AutoInstall SSL.
Sparen Sie 10% auf SSL-Zertifikate, wenn Sie noch heute bestellen!
Schnelle Ausstellung, starke Verschlüsselung, 99,99% Browser-Vertrauen, engagierter Support und 25-tägige Geld-zurück-Garantie. Gutscheincode: SAVE10