A site that loaded fine yesterday now throws a certificate warning. Or you picked the wrong certificate at a smart card prompt and the browser will not ask again. Clearing the SSL state is the standard advice for both, and it does work, but only if you clear the cache that actually holds the stale data. There are three of them, they live in different places, and every browser keeps its own copy.
This guide explains what the SSL state really is, which piece of it matches your symptom, and the exact steps for Windows, Chrome, Edge, Firefox and Safari as those interfaces look today.
The SSL state is three separate caches, not one
“SSL state” is a loose term for everything your machine remembers about past SSL/TLS connections. It covers three distinct kinds of stored data, and knowing which is which saves you from clearing the wrong one.
- The TLS session cache. The first time you connect to a site, the client and the server run a full TLS handshake and then store the result so the next connection can resume instead of repeating the work. Microsoft describes the Windows side plainly: on a first connection through the Schannel provider “a full TLS/SSL handshake is performed. When complete, the master secret, cipher suite, and certificates are stored in the session cache on the respective client and server.” Windows keeps those entries for 10 hours by default, a lifetime set by the ClientCacheTime value under HKLM\SYSTEM\CurrentControlSet\Control\SecurityProviders\SCHANNEL.
- Certificate decisions you made. Which client certificate you picked for a site, and whether you clicked past a certificate warning. These are choices, not cached cryptography, and they are stored separately from the session cache.
- HSTS entries. A site can tell your browser to use HTTPS only for a set period. Once recorded, the browser refuses to load that host over plain HTTP and shows no way to continue, which looks like a stuck cache even though it is the site’s own instruction.
The part most guides get wrong is that these caches are per-application. Chrome and Edge use their own network stack and keep their own TLS session cache; Firefox keeps its own as well. Windows keeps the Schannel cache for Windows components, Office, applications that call the Windows networking APIs, and Microsoft Edge running in Internet Explorer mode. Emptying one leaves the others untouched.
Which cache matches your symptom
- A smart card or client certificate prompt picked the wrong certificate and never came back. That is a certificate decision. On Windows, the Clear SSL state button is exactly the tool for it. In Firefox, use Site settings. In Chrome and Edge, quit the browser completely and reopen it.
- You clicked through a certificate warning and now want the warning back. Also a certificate decision. In Chrome and Edge, clear Browsing history. In Firefox, clear Site settings. On macOS, remove the trust override in Keychain Access.
- You just replaced the certificate on your own server and your browser still shows the old one. That is the session cache. Quit and reopen the browser, then re-test.
- The browser jumps to HTTPS and will not let you continue. That is HSTS, and clearing caches will not shift it. Delete the entry for that host specifically.
- Every visitor sees the error, not just you. None of the above. The problem is on the server, and no amount of local clearing will change it. Skip to the last section.
Clear the Windows SSL state
The Windows button lives in the Internet Properties dialog. Internet Explorer itself is retired, but the dialog is still part of Windows 10 and Windows 11 because Windows components, enterprise applications and Edge’s Internet Explorer mode still read its settings.
Steps
- Press Windows + R to open the Run box.
- Type the applet name and press Enter:
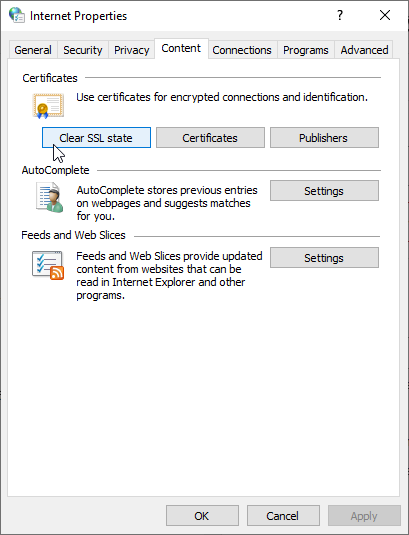
inetcpl.cpl- In the Internet Properties window, open the Content tab.
- Under Certificates, click Clear SSL state. Windows confirms that the cache was cleared successfully.
- Click OK to close the dialog.
If you prefer the graphical route, the same dialog opens from Control Panel under Network and Internet, then Internet Options. Searching the Start menu for “Internet Options” reaches it too.
What this button does and does not cover
It empties the Windows TLS session cache and, in practice, its most common effect is that the next secure connection asks you to choose a client certificate again instead of silently reusing the one you picked earlier. That is why help desks reach for it during smart card and PIV troubleshooting.
It does not clear Chrome, Edge or Firefox. Those browsers do not use Schannel for TLS; each carries its own implementation and its own session cache, so the Windows cache and the browser cache are different stores that happen to hold similar data. You will find the claim that this button clears “the SSL state for all browsers on your Windows machine” repeated across the web, and it is not accurate. Clear the browser’s own state as well, using the sections below.
It also deletes nothing from your certificate stores. Your personal certificates, your smart card certificates and the trusted root certificates stay exactly where they are.
Clear the SSL state in Chrome
Chrome holds its TLS sessions in memory, so the most complete reset is also the simplest one: close every Chrome window and reopen the browser. On Windows, check the system tray first, because Chrome can keep running in the background after the last window closes; if it does, right-click the tray icon and choose to exit before reopening.
Remove a remembered certificate warning
If you clicked Advanced and then proceeded past a certificate warning, Chrome remembers that decision for the site and stops warning you. The setting that clears it is not the cache and not cookies: it is Browsing history.
- Press Ctrl + Shift + Delete (Command + Shift + Delete on a Mac) to open Delete browsing data. You can also reach it from the three-dot menu under Settings, then Privacy and security.
- Set the time range to All time.
- Tick Browsing history. Add Cookies and other site data if you also want the site to treat you as a new visitor, and Cached images and files if you suspect a stale page rather than a stale certificate.
- Click Delete data, then restart Chrome.
Delete a stuck HSTS entry
When Chrome forces HTTPS on a host and offers no way to continue, the cause is an HSTS record rather than a cache. Open this address, type the host name into the Delete domain security policies field, and submit it:
chrome://net-internals/#hstsThe same page queries a host so you can confirm the entry is gone. Note that this only removes entries the browser learned from the site. Domains on Chrome’s preloaded HSTS list cannot be removed this way.
The one page that does not clear SSL state
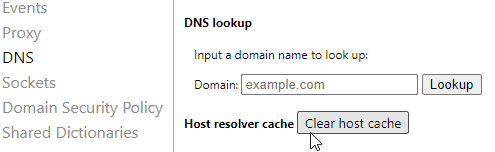
A widely copied instruction sends readers to Chrome’s DNS page and tells them to click Clear host cache:
chrome://net-internals/#dnsThat button clears the host resolver cache, which is where Chrome stores name-to-address lookups. It is genuinely useful when a site has moved to a new IP address and your browser is still reaching the old server, and it can look like a certificate fix because the old server may serve a different certificate. It does not touch TLS session data, so do not reach for it when a certificate decision is the problem.
Clear the SSL state in Microsoft Edge
Edge is built on the same engine as Chrome, so the mechanics match: its TLS sessions live in memory and a full restart clears them. The menu wording differs slightly.
- Open Settings and more (the three dots), then Settings.
- Select Privacy, search, and services.
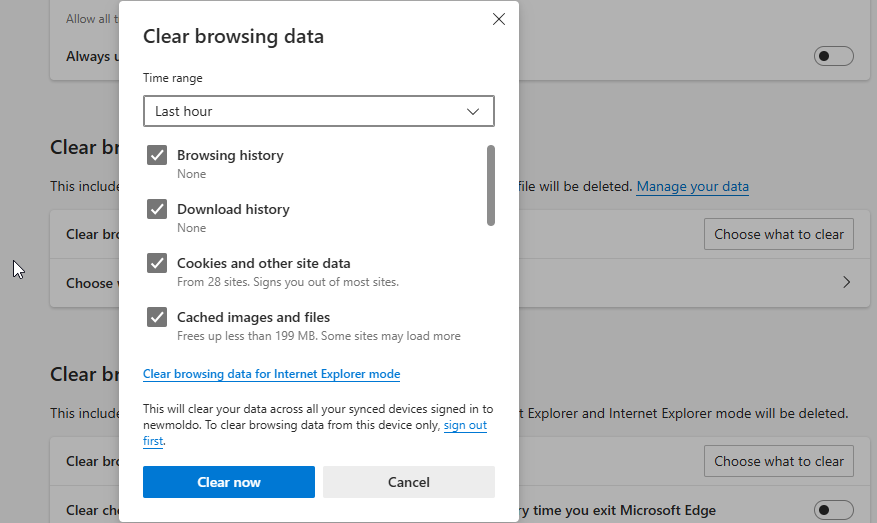
- Under Clear browsing data, click Choose what to clear.
- Set the time range to All time and tick Browsing history to drop remembered certificate warnings. Add Cookies and other site data and Cached images and files only if you want those cleared too, since neither one holds TLS session state.
- Click Clear now and restart Edge.
Edge’s HSTS page works the same way as Chrome’s:
edge://net-internals/#hstsEdge is the one browser where the Windows Clear SSL state button still matters directly, because pages opened in Internet Explorer mode run on the older engine and do use the Windows cache. If a certificate problem appears only on a site your organisation loads in IE mode, clear the Windows SSL state as well.
Clear the SSL state in Firefox
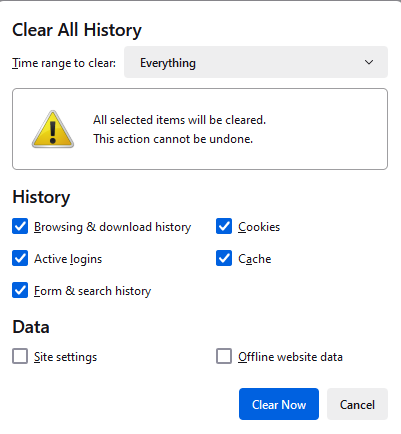
Firefox redesigned this dialog, and instructions written for the old one no longer work. The window is now called Clear browsing data and cookies, and the Active Logins checkbox that older guides tell you to tick is gone. There are five boxes, and two of them matter here.
- Press Ctrl + Shift + Delete (Command + Shift + Delete on a Mac).
- Set When to Everything.
- Tick Cookies and site data. This is the box that clears Firefox’s TLS session resumption tickets, and it clears HSTS entries at the same time. Firefox groups those tickets with site data rather than with caches on purpose, because a server can recognise a returning client by the same ticket, which makes them closer to a cookie than to a cached image. Expect to be signed out of sites.
- Tick Site settings if the problem is a certificate decision. This is the box that clears remembered certificate exceptions and the record of which client certificate you chose. It also resets site permissions such as camera and notification access.
- Click Clear, then restart Firefox.
Temporary cached files and pages is the box people tick by habit, and it is the wrong one for this job. It holds page resources, not TLS state. Ticking it does no harm, it simply will not fix a stuck certificate.
To target a single site instead of everything, open the history sidebar or library, right-click the site and choose Forget About This Site. That clears the same data for that host alone.
Clear the SSL state in Safari on macOS
Safari has no SSL state button, and macOS does not expose one either. Quitting Safari with Command + Q and reopening it is the practical equivalent for session data, because the session cache does not survive the application.
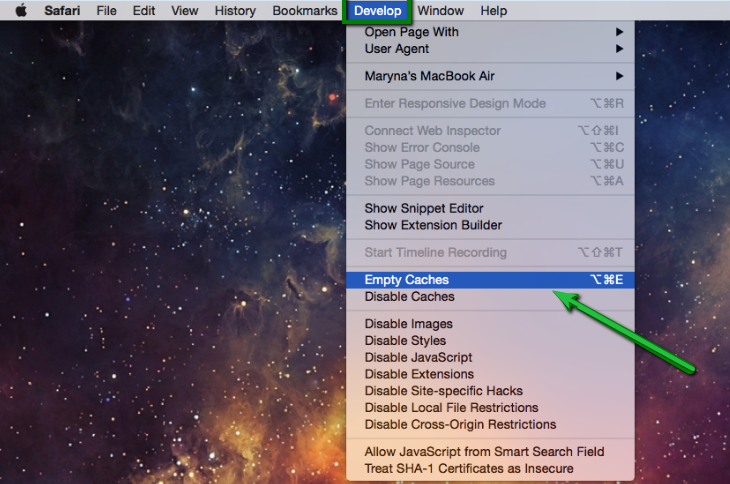
For page resources, the Develop menu has an Empty Caches command. Two labels changed here, so older instructions send you looking for controls that no longer carry those names.
- Choose Safari, then Settings in the menu bar, or press Command + comma. The window was called Preferences before macOS Ventura.
- Open the Advanced tab and tick Show features for web developers. On older releases this checkbox read “Show Develop menu in menu bar”.
- Close the window. Choose Develop, then Empty Caches.
Be clear about what that gets you: it empties Safari’s web content caches, not TLS session state and not any certificate decision.
Remove a certificate trust override
When you click past a Safari certificate warning, macOS records a trust override in your login keychain, and it survives restarts. Remove it in Keychain Access, which still ships with macOS but is no longer in Applications, then Utilities. Since macOS Sequoia it sits in a system folder, so open it with Spotlight (Command + Space, then type Keychain Access) or from Terminal:
open -a "Keychain Access"Select the login keychain, choose the Certificates category, find the entry for the site, and delete it. Safari will show the warning again on your next visit.
When clearing the SSL state will not fix anything
Clearing local state only helps when the stale data is local. If the certificate itself is wrong, every visitor sees the same error and no local change will help. Check the site with the SSL Checker before spending time on your own machine. These cases are server-side:
- The certificate has expired or is not valid yet. See NET::ERR_CERT_DATE_INVALID.
- The chain is incomplete because the server does not send the intermediate certificate. This is the most common cause of a trust error that appears on some devices and not others. See NET::ERR_CERT_AUTHORITY_INVALID and SEC_ERROR_UNKNOWN_ISSUER.
- The name does not match. The SSL certificate was issued for a different host name than the one in the address bar. See NET::ERR_CERT_COMMON_NAME_INVALID.
- The certificate is self-signed on a device or internal service. No client trusts it until you install the issuing certificate, and clearing state only brings the warning back sooner.
One more habit worth dropping: clearing the SSL state on a schedule does nothing for your security. Session tickets already expire on their own, on Windows after 10 hours by default, and a cached session cannot be used to reach a site you were not already authorised to reach. Clear it when you are troubleshooting a specific symptom, not as routine maintenance.
Frequently Asked Questions
No. Nothing is removed from any certificate store. The Windows button clears cached TLS session data and the record of which client certificate you selected. Your personal certificates, smart card certificates and trusted roots are untouched, which is why the next connection can prompt you to pick a certificate again rather than failing outright.
Because Chrome does not use the Windows TLS implementation. It ships its own, with its own session cache, so the Windows button and Chrome’s cache are separate stores. The same is true of Edge for ordinary browsing and of Firefox. The exception is Edge running a page in Internet Explorer mode, which does use the Windows cache. Clear the browser’s own state using the steps above.
Clear Browsing history in Delete browsing data, then restart Chrome. That is the setting Chrome ties the remembered decision to, which surprises people who assume it lives with cookies or the cache. In Firefox the equivalent box is Site settings, and on macOS you remove the trust override from your login keychain in Keychain Access.
It no longer exists. Firefox replaced the old Clear Recent History window with a dialog called Clear browsing data and cookies, which offers Browsing & download history, Cookies and site data, Temporary cached files and pages, Site settings and Saved form info. For SSL state, Cookies and site data covers session tickets and HSTS, and Site settings covers certificate exceptions and client certificate choices.
There is no macOS equivalent of the Windows button. Quit the browser fully with Command + Q and reopen it, which drops the in-memory session cache. In Chrome, Edge and Firefox on macOS, the same clearing dialogs described above apply, reached with Command + Shift + Delete. For a certificate warning you accepted in Safari, delete the entry from the login keychain in Keychain Access.
No. An expired certificate is served by the site, so the error follows the certificate rather than your machine, and it appears for every visitor. Clearing local state can help in one narrow case: you renewed the certificate on your own server minutes ago and your browser is still resuming an older session. Confirm what the server is actually sending with the SSL Checker first.
Only when you are troubleshooting. Cached sessions expire by themselves, the Windows default being 10 hours, and holding one grants no access you did not already have. Regular clearing costs you a full handshake on every first connection and buys nothing in return.
For certificate errors that turn out to be server-side rather than cached, see our guides to SSL connection errors, including Your connection is not private and ERR_BAD_SSL_CLIENT_AUTH_CERT for client certificate failures. Background on how the underlying session keys are negotiated is in our public key cryptography explainer.
Save 10% on SSL Certificates when ordering from SSL Dragon today!
Fast issuance, strong encryption, 99.99% browser trust, dedicated support, and 25-day money-back guarantee. Coupon code: SAVE10